7 mins read
Money now moves in seconds. India’s UPI processed about 186 billion transactions in the year to March 2025. Brazil’s Pix handled nearly 80 billion in 2025. In the US, The Clearing House’s RTP network moved more than $1.3 trillion in the first eleven months of 2025, over five times its total for 2024.
Speed is the selling point. It is also the weak spot. A card payment can be disputed and reversed. An instant payment usually cannot. Once the money lands, it is gone.
So we asked industry leaders a simple question: as real-time payment rails grow, what fraud patterns are emerging that traditional rules-based systems miss?
Fintechbits analysis
Why the old rules fall short
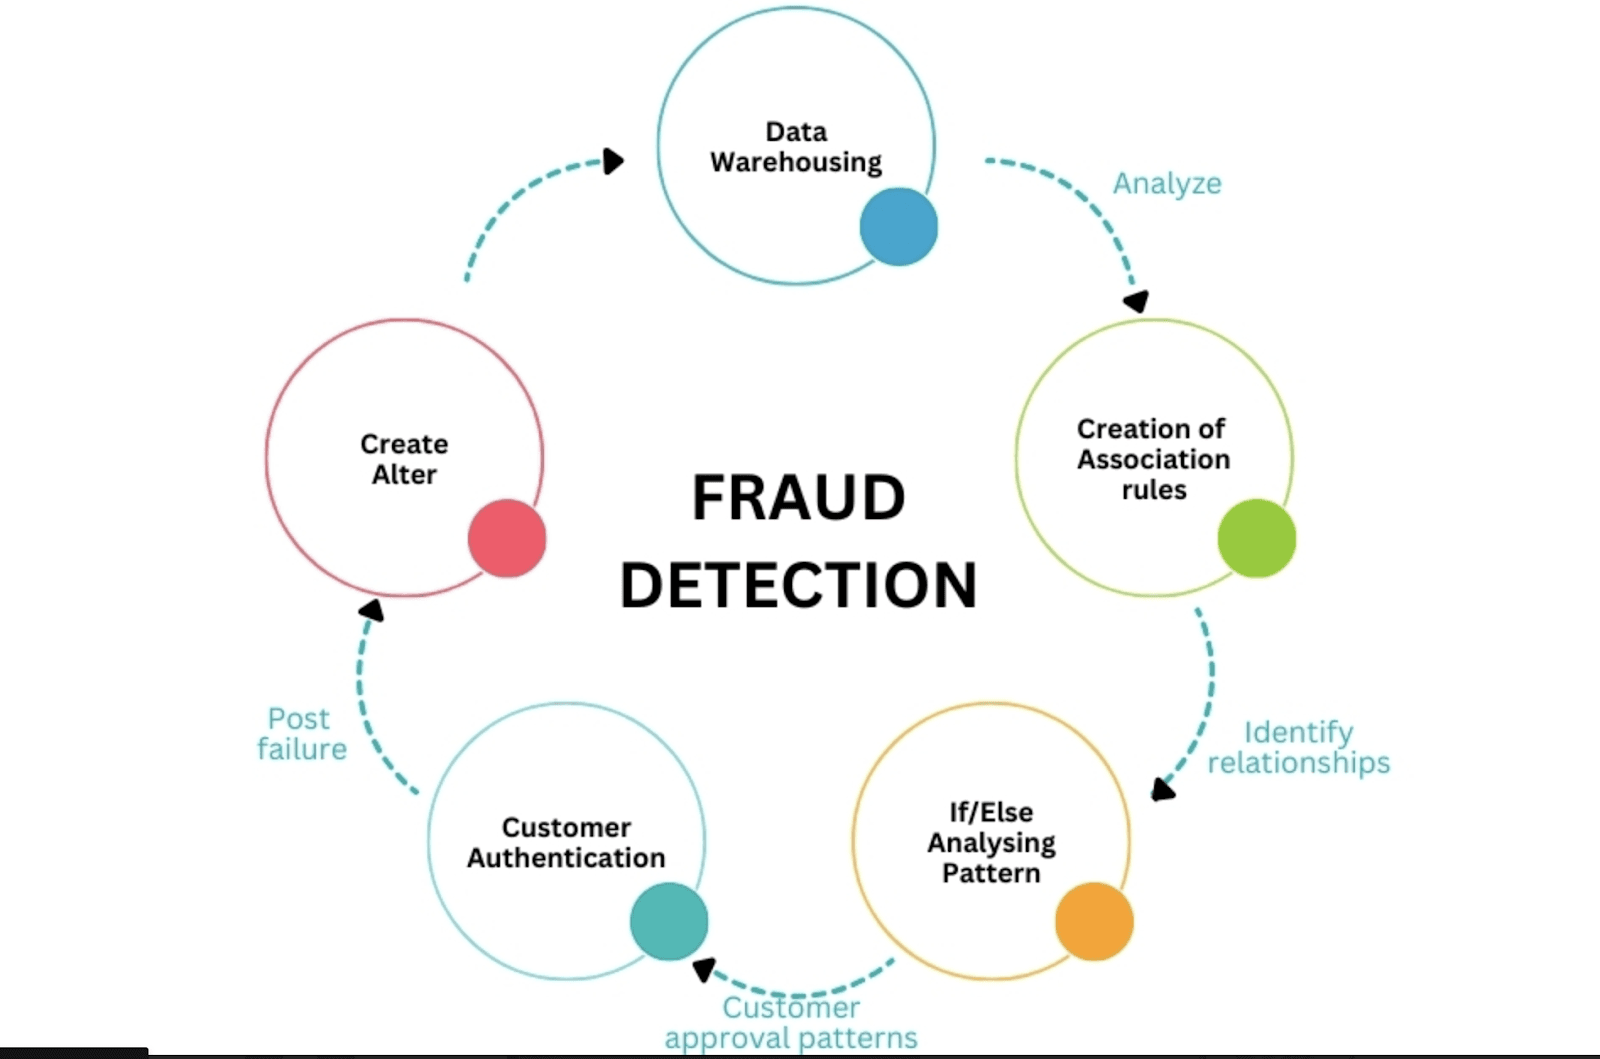
Most fraud systems still lean on rules. If a payment is too large, too frequent, or comes from an odd location, flag it. That approach worked when fraud mostly meant a stranger using stolen card details.
Instant rails expose three weaknesses. First, there is almost no time to decide. A check must finish in seconds, before the payment settles. Second, criminals learn the limits. They test the system, then keep each payment just below the line. Third, each bank sees only its own piece of the puzzle. A rule at one bank cannot see stolen money being split across ten others.
“Static, rules-based payment fraud systems do not adequately detect fraud in today’s digital world because they evaluate individual transactions in isolation rather than evaluating them as part of a more comprehensive, ongoing assessment of the user’s behavior and history. From my involvement in enterprise architecture, I immediately recognize this limitation; thus, while an abnormal or large monetary transaction may trigger some static threshold-based detection rule, that same static rule will not detect low-and-slow account takeover attacks. In cases of account takeover fraud, for example, the fraudster will often take over a victim’s account remotely via a legitimate device session, make several small inconspicuous changes to the victim’s account to establish trust with the account, and then eventually execute a large transaction at some point in the future, after the victim’s activity has decreased significantly, causing the large transaction to trigger no alarms in a static rule-based filter. Therefore, static, rules-based systems treat each transaction as a discrete event and ultimately do not account for all of the preceding behavioral activity that led to that single transaction. I am redesigning financial enterprise architectures using both the NIST and OWASP architecture frameworks to ultimately implement a behavioral response system. I am doing this by moving away from simple if/then rules to assessing intent of the transaction based on behavioral characteristics, such as device health, behavioral biometrics (e.g., keystroke cadence or mouse movement), and historical context. If any aspect of the most recent behavioral activity deviates from the established behavior of the user, the system must automatically increase the risk score, irrespective of the transaction amount. Detecting fraudulent transactions will be transitioned away from creating better rules and instead will involve establishing all of the complete truth related to the transaction to provide users with a transparent experience and to interdict threats in real-time. Moving toward an adaptive, machine learning-based risk scoring system will allow for a greater understanding of the user’s journey as a complete and validated signal.”
Sudhanshu Dubey, Delivery Manager, Enterprise Solutions Architect, Errna
The account takeover pattern he describes is growing. In the Federal Reserve’s 2026 Risk Officer Survey of 403 US financial institutions, the share reporting account takeovers rose 7%. Faster payments also showed the biggest jump in fraud attempts of any payment type.
Fake people, real accounts
The second shift is in who opens the accounts. Generative AI makes it cheap to produce convincing fake identities at scale. Entrust’s 2026 Identity Fraud Report found deepfakes in one in five biometric fraud attempts. Injection attacks, where fake images are fed straight into a verification system, rose 40% in a year.
“I’m seeing an increase in these AI-synthesized identity attacks that look like a human and bypass velocity and IP checks. Classic rule sets fail to catch instances when a single app template generates a huge amount of realistic-looking identities across a variety of addresses and networks. Deepfake documents and generated identity narratives render alone document verification moot, which is where a layered approach becomes critical. Personally, I believe applying behavioral biometrics over document verification, plus retraining models on a consistent basis, turns every instance of fraud into a signal rather than an anomaly.”
Abhinav Gupta, Founder, Profitjets
Standard setters agree that one check is no longer enough. NIST’s updated digital identity guidelines, finalised in July 2025, add defences against deepfakes and injection attacks on top of document checks rather than replacing them. The direction is clear: more layers, not fewer.
This matters for instant payments because fake identities often become mule accounts, the landing spots for stolen money.
The fraud that looks completely normal
The biggest blind spot is one where nothing looks wrong at all. In an authorised push payment (APP) scam, the real customer sends the money themselves. A scammer has convinced them they are investing, helping a partner, buying something, or moving savings to safety.
The UK publishes the clearest data. APP scam losses rose 19% to £576.4 million in 2025, according to UK Finance. Investment scams jumped 40% to £221.5 million. Over the same period, unauthorised fraud fell 5%. Criminals are shifting from stealing access to manipulating people.
Rules struggle here because every signal checks out. Right person. Right device. Right password. Romance scam victims make around ten payments before they realise, each one small enough to pass. Behavioural tools can still help, but only if they look for signs of pressure, such as hesitation while typing or an active phone call during a payment, rather than signs of a stranger.
Follow the money
Once a scam payment lands, it moves fast. Brazil’s central bank found its Pix refund mechanism recovered only 9.3% of disputed value in 2025, because stolen funds were quickly scattered across many accounts.
Countries are responding by targeting the receiving end. Brazil’s upgraded MED 2.0 system traces funds beyond the first account. India’s central bank has rolled out MuleHunter.AI, an AI model that spots mule accounts, to 26 banks. The UK now makes the receiving bank pay half of every reimbursed scam, which gives it a direct reason to stop mules.
What works now
No single tool solves this. The approaches showing results work in layers:
- Check the payee. The EU made Verification of Payee mandatory for euro transfers on 9 October 2025. It warns the sender when the name does not match the account.
- Score the receiver, not just the sender. Network-level tools rate the account receiving the money using data from many banks.
- Watch behaviour over time. Look at the full customer journey, not one payment in isolation.
- Share data. Banks, telecom firms and online platforms each see part of a scam. None sees all of it.
Regulation is pushing in the same direction. The UK’s mandatory reimbursement scheme returned 88% of in-scope losses to victims in its first year. Australia’s Scams Prevention Framework covers banks, telecoms and digital platforms, with penalties of up to A$50 million per breach. The EU has agreed new payment rules that will make providers refund victims of bank impersonation scams.
The US is earlier on this curve. The Federal Reserve’s survey calls instant payments a “relative bright spot” for now, with few reported attempts and losses. That gives US institutions a window to learn from markets that are further ahead.
The bottom line
Real-time payments did not invent fraud. They removed the time to catch it. Better rules alone will not close that gap, because the most damaging scams break no rules. The answer lies in context: who is sending, who is receiving, what happened before, and what other institutions can see. Speed is now the standard. Fraud prevention has to keep pace.
FintechBits covers payments, banking and fintech developments for readers in the US and UK. This article is for information only and is not financial advice. Views expressed are those of the FintechBits editorial team.