5 mins read
Dateline: Fingerprint, research report, 14 October 2026
Fingerprint, the Chicago-based device intelligence company, published its 2026 State of AI Traffic in Financial Services report on 14 October 2026, finding that 79% of 300 US financial services leaders had detected a malicious bot or scraper slipping past a perimeter defence by posing as a legitimate AI assistant or search crawler. Fintechbits found a 50-point gap inside the Fingerprint survey: 95% of the 300 financial services leaders said they could tell genuine AI assistants from spoofed traffic, but only 45% said they detect spoofed AI traffic bypassing their defences and mitigate it in real time. The research was carried out by Censuswide between June and August 2026, according to the release.
What the Fingerprint survey found
The headline figure is the 79% who have seen a bot or scraper get through by spoofing an AI assistant or search crawler identity. The rest of the Fingerprint survey describes why. Just 26% of respondents said they have full visibility into automated traffic that bypasses client-side JavaScript detection, while 61% still rely on client-side JavaScript tags or native SDKs to detect bots.
Put those two numbers together and the gap is easy to see. Many AI agents talk to websites and APIs through direct HTTP requests that never run JavaScript, so a detection tag in the browser never fires. Only 43% of respondents said they verify traffic against authorised IP ranges or DNS in real time.
The traffic itself keeps growing. In the Fingerprint survey, 95% of respondents reported more automated traffic hitting their web properties and APIs over the 12 months before fieldwork, and 70% said they could not guarantee consumer data privacy compliance without verifying automated traffic at the HTTP level.
How firms are responding to AI traffic
Few firms want to block everything. Forty per cent of respondents said their main fear is blocking a legitimate consumer AI assistant and pushing customers to a competitor that allows it. Fintechbits has covered the same tension from the other side, in Experian and Fastly’s work on agent trust for AI commerce.
Spending plans follow from that. The Fingerprint survey says 32% rank real-time IP-range and DNS verification of AI provider networks as their top priority for the following year, and 46% call edge-deployed, no-JavaScript identification a critical or high-priority project that is already planned or funded for the next six to 12 months.
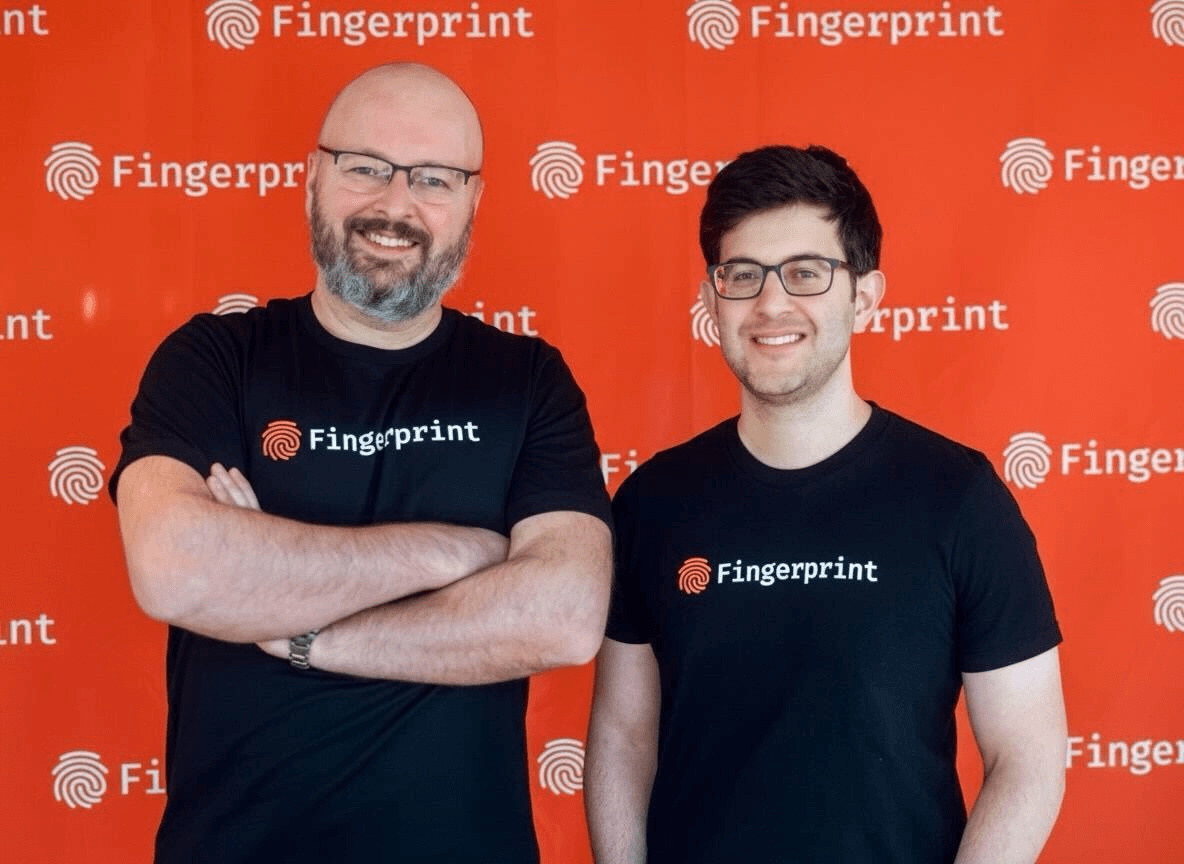
Dan Pinto, Fingerprint’s chief executive and co-founder, puts the shift simply: “Financial institutions built their defenses for a web where humans opened browsers that executed JavaScript.”
Fintechbits analysis
Fintechbits analysis
Why the Fingerprint survey’s confidence gap matters
The 50-point gap is the most useful number in the Fingerprint survey. Ninety-five per cent confidence next to 45% real-time mitigation means most firms believe they can spot an impostor but cannot reliably stop one while it is happening. That is a familiar pattern in fraud: detection after the fact feels like control, and the loss has already happened.
Read the source with care. Fingerprint sells device intelligence and bot detection, the report is the vendor’s own, and its recommended fix lines up with the kind of server-side identification Fingerprint markets. The methodology is disclosed, which helps, but respondents self-reported their own capabilities. The 26% full-visibility figure is probably the most candid number in the report, since respondents had little reason to understate their own coverage.
Whoever paid for the research, the risk it describes is there. Banks are about to field traffic from customers’ own AI assistants checking balances or moving money, and they will need to tell those apart from scrapers wearing the same user agent. Fintechbits has looked at the limits of rules-based fraud systems in instant payments, and agent traffic adds another layer to that problem.
Frequently asked questions
What did the Fingerprint survey find?
The Fingerprint survey of 300 US financial services leaders found that 79% had detected a malicious bot or scraper bypassing perimeter defences by spoofing a legitimate AI assistant or crawler. Only 26% said they had full visibility into automated traffic that bypasses client-side JavaScript detection.
Who carried out the research?
Censuswide surveyed 300 US financial services leaders between June and August 2026, including CISOs, chief risk officers and fraud strategy heads. Respondents came from retail banking, fintech, wealth management and investment banking.
Where is the gap in banks’ AI traffic defences?
Fintechbits found a 50-point gap in the data: 95% of respondents said they could tell genuine AI assistants from spoofed traffic, but only 45% said they detect and mitigate spoofed AI traffic in real time. Confidence in spotting impostors runs well ahead of the ability to stop them.
What to Watch Next
The 46% of respondents who say edge-based, no-JavaScript identification is planned or funded for the next six to 12 months set a testable marker. Watch whether large banks start publishing how they verify AI agent traffic, and whether supervisors begin asking for it in fraud and data-protection reviews.
Why this matters
Fintechbits found a 50-point gap inside the Fingerprint survey: 95% of 300 US financial services leaders said they could tell genuine AI assistants from spoofed traffic, but only 45% detect and mitigate it in real time. Seventy-nine per cent have already seen a bot slip through by impersonating an AI assistant, and 61% still rely on JavaScript-based detection that agent traffic skips. The survey is vendor-commissioned, so the gap matters more than the headline.
Primary sources
businesswire.com | PRESS RELEASE | https://www.businesswire.com/news/home/20261014510496/en/Fingerprint-Report-4-Out-of-5-Financial-Institutions-Have-Detected-Security-Perimeter-Bypasses-From-AI-Spoofed-Traffic
fingerprint.com | COMPANY WEBSITE | https://fingerprint.com